Snelling Achieves Prestigious ISO 27001 Certification.
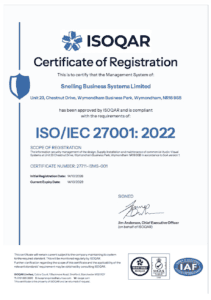
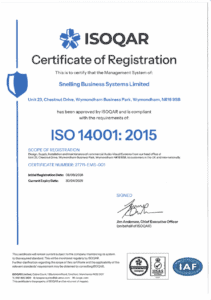
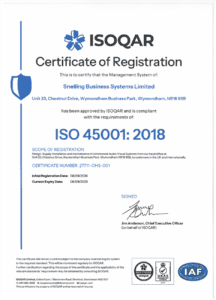
Snelling is delighted to announce that it has achieved ISO 27001 certification, the internationally recognised standard for information security management.
Achieving this prestigious certification required Snelling to undergo a rigorous process of identifying and managing information security risks, implementing robust security controls, establishing clear policies and procedures, and ensuring all staff understand their responsibilities and are trained in how to handle data. Compliance is independently assessed through a comprehensive external audit, with ongoing reviews required to maintain certification.
For our clients, ISO 27001 provides independent assurance that Snelling takes information security seriously, with effective systems in place to protect sensitive information, minimise cybersecurity risks and continually improve security practices.
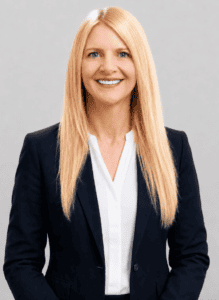
Pauline Grieve, Chief Operating Officer and Director, who led this project for Snelling commented:
I am incredibly proud that Snelling has achieved ISO 27001 certification. This has been a significant project for the business and has involved a huge amount of work to ensure information security is firmly embedded within our day-to-day operations. Achieving certification gives our clients additional confidence in how seriously we take the security and protection of their information, and it is a real credit to everyone at Snelling who has contributed to getting us here.